Continuous Threat Exposure Management, or CTEM, has become one of the most widely adopted frameworks in enterprise security. Organizations have invested heavily in exposure management platforms, deployed continuous discovery, and stood up dashboards that surface exposure across the environment. Yet many of these same organizations report a frustrating outcome: significantly more visibility, without a corresponding improvement in risk reduction.
At Inspire, we see a consistent reason for this gap. CTEM is frequently implemented as a technology initiative when it is fundamentally an operating program. The distinction determines whether an exposure management investment produces results or simply produces reports.
A capable exposure management platform can scan, correlate, score, and present exposure with impressive fidelity. What no platform can do is establish who owns a given remediation, determine what gets prioritized when competing exposures demand the same limited resources, resolve the situation when an owner lacks capacity, or translate a technical finding into a business decision that a leader will stand behind. These are not gaps waiting to be closed in a future software release. They are the responsibilities of an operating model, and building an operating model is organizational work.
The CTEM lifecycle is commonly described in five stages: scoping, discovery, prioritization, validation, and mobilization. Tooling maturity is concentrated in the earlier, more technical stages. Discovery and validation are well served by modern platforms. Mobilization, the stage at which exposure is driven down through ownership, coordination, and follow-through, is the least automated and the most dependent on people and process. It is also, in our experience, the stage where programs most often stall.
This has a clear implication for security leaders. The stage that most determines whether a CTEM program delivers value is the stage that tooling supports least. Organizations that concentrate their energy on platform selection and discovery coverage, while under-investing in ownership, cadence, and decision rights, tend to build programs rich in findings and poor in outcomes.
A durable CTEM program depends on several elements that exist outside the toolset. It requires clear ownership, a named individual with genuine authority to drive remediation, rather than diffuse responsibility spread across multiple teams. It requires prioritization grounded in business context, so that decisions reflect what a system means to the business rather than severity scores alone. It requires an operating cadence, a recurring rhythm in which open exposures receive sustained attention until they are resolved. And it requires deliberate ownership of the handoffs between security and the business, where remediation frequently stalls when no one owns the translation from technical finding to business action.
For security leaders evaluating the health of an exposure management program, we recommend a simple diagnostic question: when an exposure is validated, what happens next, specifically? A clear, owned, time-bound answer indicates a functioning program. A vague answer indicates that the investment has produced visibility without management, and that the path forward is unlikely to be another tool.
Inspire helps organizations close exactly this gap, turning exposure management from a tooling initiative into an operating program that produces decisions, accountability, and sustained risk reduction. If your program has visibility but not traction, the opportunity is almost never in the dashboard. It is in the operating model beneath it.
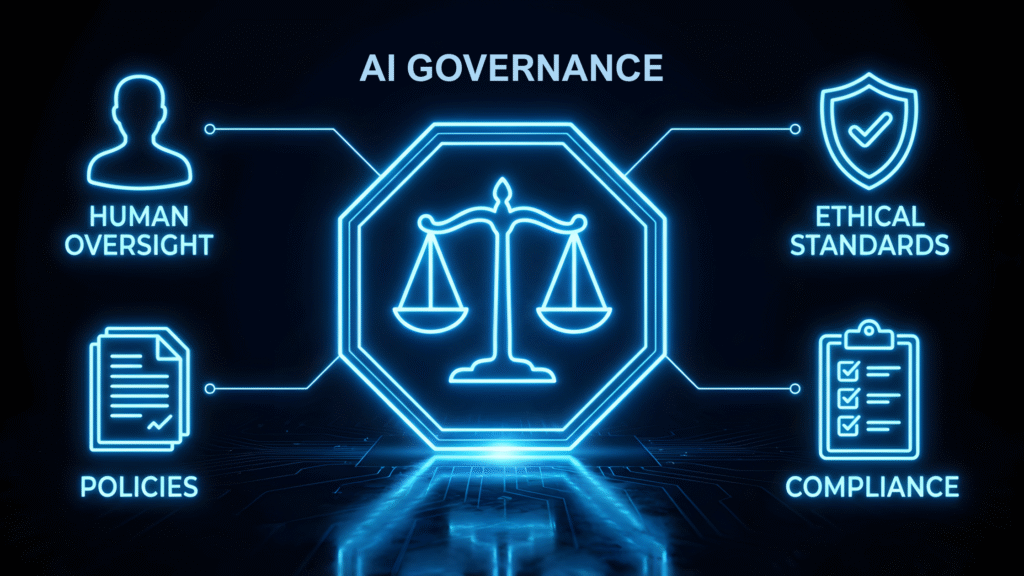
Artificial intelligence is moving into business operations faster than most organizations can govern it.
In response, many companies are rushing to create AI policies, approval committees, security requirements, and compliance frameworks. Those efforts are understandable. AI introduces real risks involving data, model performance, automated decisions, cybersecurity, privacy, regulatory exposure and third-party vendors.
But many organizations are beginning in the wrong place.
They are selecting controls before they clearly understand their AI risk. They are treating governance as a compliance exercise rather than an operating model. And in their attempt to gain control, they are creating processes so restrictive that employees and business teams begin working around them.
The central question should not be, “How do we control AI?” It should be “How is AI affecting our business, where4 can it cause harm, and what level of risk are we prepared to accept?
Until an organization can answer those questions, it cannot build effective AI governance.
Instead of AI Governance Being Built Around Controls, It Should Begin with Risk
The core problem is that many companies do not yet understand their AI exposure. That matters because risk should drive security and governance requirements. Without a clear understanding of the potential impact, organizations tend to adopt controls that do not match their actual exposure.
Some controls become unnecessarily burdensome. Others fail to address the most consequential risks. For example, the level of governance required for an employee using AI to summarize public information should not be the same as the governance required for an AI system that influences hiring, healthcare, credit, legal decisions, or access to essential services.
The organization must first understand:
These are not simply technical questions. They are business-risk decisions.
The organizations approaching AI governance most effectively are incorporating risk management at the beginning of adoption rather than trying to retrofit governance3 after systems and workflows are already in use.
AI Governance Is Not a Compliance Checkbox
Another common mistake is treating AI governance as a legal, compliance or IT project. It is all those things and more.
Effective governance must account for model risk, data risk, cybersecurity risk, decision risk, privacy, third-party exposure, ethical considerations, and the legal consequences of AI-assisted outcomes.
AI governance must operate across the organization:
When one of these groups is absent, the organization develops a governance gap.
An AI policy may satisfy the need to show that the company has addressed the issue. But establishing a policy is not the same as building governance.
Real governance requires an operating structure. Who evaluates a new AI use case? Who approves a third-party tool? Who determines whether a use case requires a full risk review? Who responds when an AI system produces a harmful or incorrect outcome? Who can stop deployment?
Without clear answers and enforceable processes, the policy is largely decorative.
Better Models Do Not Compensate for Weak Environments
Organizations often focus heavily on model selection and performance. Those factors matter, but the model is only one component of the risk.
A mediocre AI model operating within a well-governed environment can be safer than a highly capable model operating in a poorly controlled environment.
The surrounding operating environment determines:
This is why broad statements such as “a human will review the output” are not sufficient.
Human-in-the-loop controls only reduce risk when the review is meaningful, selective, and supported by objective validation criteria. If employees ar asked to approve every output without adequate context, testing standards or clearly defined escalation requirements, human review becomes a procedural formality rather than a reliable safeguard.
Governance cannot depend entirely on a person remembering to pause, interpret a policy and make the right decision under operational pressure.
Where possible, controls should be embedded directly into the systems, workflows and delivery pipelines in which AI is used.
Governance that exists outside the work is governance that will eventually be skipped.
Over-restriction Can Make AI Risk Harder to Control
One of the most persistent beliefs in enterprise AI adoption is that tighter restriction create greater control.
In many companies, the opposite is true. Risk does not come simply from employees using AI. It comes from uncontrolled use of it. Controlled use is visible, monitored and governed. The organization knows which tools are being used, what information is entering them, which decisions they influence and who owns the associated outcomes.
When AI is restricted without giving employees a practical approved alternative, usage does not necessarily stop. It moves underground.
Employees turn to consumer AI accounts, unauthorized tools, browser extensions, embedded software capabilities, and external platforms that have not gone through security, privacy, or vendor-risk review. The organization has not eliminated the exposure. It has eliminated its own visibility into exposure.
This is the foundation of shadow AI. Overly complicated review processes can produce the same result. If every AI use case must wait for a centralized governance board that meets infrequently, business teams will either move ahead without approval or find a faster path outside the established process.
Approval queues do not scale at the speed of adoption. Governance therefore must be proportional. Low-risk applications should have a lighter path than high-impact use cases. Controls should be strong where the consequences justify them, but simple enough that employees have realistic reason to follow the approved process.
Governance should function as a lane marker, not a permanent brake.
You Cannot Govern AI You Do Not Know Exists
Many organizations cannot produce an accurate list of the AI tools, models, integrations, and use cases already operating.
Some are formally approved. Others are introduced by individual teams or added through existing software vendors. As AI becomes embedded into more platforms, even defining what counts as an AI use case becomes more difficult.
That is why an AI inventory cannot be a one-time exercise. It must be maintained as an ongoing operational capability.
At a minimum, the inventory should identify:
Without that visibility, organizations cannot consistently assess risk, review vendors, monitor performance or enforce data-handling requirements.
Governance Requires Clear Ownership
AI governance often stalls because everyone agrees it is necessary, but not on has clear accountability for it.
Committees can provide oversight, but they do not replace named ownership. Someone must have authority over the governance program, and each AI use case must have a business owner accountable for its outcome. Executive must also define acceptable risk.
How accurate is accurate enough? Which decisions can be automated? When is human review required? What happens when speed conflicts with risk tolerance?
These are leadership decisions.
The hardest part of AI governance is turning ambiguity into decision the business is willing to enforce.
A Practical Starting Point
Companies do not need a complex enterprise framework on day one. A practical starting point includes five steps:
From there, controls should be embedded into the points where AI is purchased, developed, deployed, and monitored.
The goal is to make responsible AI use easier to approve, maintain and sustain. The companies that succeed will be the ones that understand their risk, make clear decisions and operationalize governance from the beginning.
For nearly two decades, vulnerability management has followed a familiar pattern: identify vulnerabilities, assign severity scores, prioritize remediation, and patch within established service-level agreements.
That model was built for a world where attackers operated at human speed. Today, that assumption is becoming increasingly dangerous.
Recent advances in AI-powered vulnerability research suggest that organizations may be entering a period where software flaws can be discovered, analyzed, chained together, and weaponized far faster than traditional security programs were designed to handle. While the number of vulnerabilities continues to grow, the more significant change is the shrinking amount of time defenders have to respond.
As AI accelerates vulnerability discovery and exploit development, security leaders must focus on rapidly identifying exploitable exposures and reducing the time between discovery and mitigation.
What Changed?
Several developments over the past year have fundamentally altered the vulnerability landscape.
Most vulnerability programs were designed around three assumptions:
Assumption 1: Severity equals risk
Many organizations still prioritize vulnerabilities primarily using Common Vulnerability Scoring System (CVSS) scores.
The problem is that CVSS was never designed to measure actual business risk.
The Exploit Prediction Scoring System (EPSS), developed by FIRST, was created specifically because severity scores alone are poor predictors of real-world exploitation. EPSS estimates the likelihood a vulnerability will be exploited within the next 30 days.3
CISA similarly directs organizations to incorporate its Known Exploited Vulnerabilities (KEV) Catalog into prioritization decisions because KEV tracks vulnerabilities that are actively exploited in the wild.4
Assumption 2: Vulnerabilities are evaluated individually
Attackers rarely think this way. A medium-severity vulnerability that appears insignificant on its own may become highly dangerous when combined with:
AI systems are increasingly capable of discovering these attack chains faster than human analysts.5
Assumption 3: Monthly scans and 30-day SLAs provide sufficient protection
Monthly scanning schedules and 30-day patch SLAs emerged during an era when discovery, exploit development, and attacker operations all required substantial human effort.
Today's threat landscape increasingly includes automation on the attacker side.
When AI can identify vulnerabilities continuously and assist in exploit development, quarterly assessments, monthly scans, and static patch cycles create growing exposure windows.6
What Leaders Should Measure Instead
The most important shift is moving from measuring vulnerability counts to measuring exposure.
What Leaders Should Do Now
Organizations do not need to wait for a complete transformation to improve resilience. Several practical actions can be implemented immediately.
What Large Organizations Are Already Doing
Executive Takeaway
Vulnerability management is undergoing a fundamental shift. For years, organizations focused on how many vulnerabilities they had and how quickly they could deploy patches.
In an era where AI can discover vulnerabilities that survived decades of review and assist in exploit development at unprecedented speed, the organizations best positioned to succeed will be those that understand their true exposure, prioritize risk in context, and rapidly reduce opportunities for attackers. In this new environment, resilience is increasingly defined by how quickly an organization can identify, validate, and mitigate exploitable risk.
1 Project Glasswing: Securing critical software for the AI era \ Anthropic
2 https://www.securityweek.com/google-detects-first-ai-generated-zero-day-exploit/
3https://www.first.org/epss/model
4 Known Exploited Vulnerabilities Catalog | CISA
5https://red.anthropic.com/2026/mythos-preview/
6 AI shrinks zero-day exploit time from a year to a single day, heading toward one minute — Zero-Day Clock warns security window has collapsed | Tom's Hardware
7 https://blog.cloudflare.com/cyber-frontier-models/
8 https://blog.mozilla.org/security/
9 https://www.cisa.gov/known-exploited-vulnerabilities-catalog
It starts as a cutting-edge AI capability designed to transform the business, whether through an AI assistant supporting customers or automation tied into core systems. It means faster decisions, less manual work, and the kind of innovation that makes leadership lean in and say, “this is where we need to go.” They are not wrong, but what many do not stop to define is what else it can do and what could happen if the wrong person, agent, or system gains access. This is where things begin to unravel.
When Partner Access Becomes the Entry Point
Just last week, Mythos, a powerful AI model from Anthropic was made available to a limited group of external partners.1 These partners had mature security practices with existing agreements containing defined access requirements. On paper, it looked controlled. There was restricted access, defined use cases, and a carefully managed rollout. However, days later, Bloomberg News reported a small number of people had been sharing access to the model with others whose environments did not have the same level of protection. Anthropic is now investigating potential unauthorized access through third-party contractors.
The AI itself wasn’t necessarily the weak point, but poorly managed access permissions within its implementation were.
If that feels distant, it shouldn’t. Most companies integrating AI today are doing the same thing. They are connecting it to vendors, tools, and external systems that don’t operate under the same environment.
When Access Boundaries Fail by Design
In early 2026, an issue with the AI coding platform Lovable showed how quickly things can go wrong when access is not clearly defined. 2 A regular user discovered they were “able to access another user's code, AI chat histories, and customer data,” not through hacking, but simply by using the system as it was built. The exposure wasn’t limited either, reportedly “affecting every project created before November 2025,” pointing to a broader structural problem rather than a one-off defect. Lovable later acknowledged that “while unifying permissions in our backend, we accidentally re-enabled access to chats,” reinforcing that this was not an advanced attack but a breakdown in access control during its own implementation. Security experts called it “another unfortunate example of lacking secure defaults” and “a failure to threat model for the automated AI age.”
This highlights a deeper issue because the AI platform prioritized ease of use and rapid development without clearly defining who should have access to what. As one expert put it, “If users can accidentally expose sensitive data… attackers don't need to hack anything at all.” This is exactly the kind of risk that emerges when AI capabilities are deployed before access boundaries and controls are clearly and consistently established.
When AI Agents Become an Open Door to Your Entire System
In early 2026, researchers uncovered tens of thousands of AI agents deployed across enterprise environments.3 These weren’t experimental tools sitting in isolation. They were active, connected, and in many cases, publicly exposed, making them vulnerable to takeover. In some cases, attackers could gain control and use the agents to access email, files, and internal systems.
Jeremy Turner, VP of Threat Intelligence at SecurityScorecard stated, “The risk isn’t that these systems are thinking for themselves. It’s that we’re giving them access to everything. It's like handing your laptop to a stranger on the street and hoping nothing bad happens.”
The problem in most of these cases was the absence of basic controls that every organization already knows how to implement. The AI agents were given broad, system-level permissions without restriction, exposed without proper network controls, and deployed without secure configuration standards. When foundational controls like least privilege, network access restrictions, and system hardening are skipped, AI not only introduces risk, but it also amplifies it at scale.
Conclusion: Define the Risk Before You Deploy
A traditional vulnerability might expose information, but an exposed AI agent can act quickly, repeatedly, and across systems. It’s not just a door left open, but something inside the building that can move around like a person can. Across these incidents, the pattern is simple but often overlooked. No one clearly defined the risk before deployment in a way that answered:
Instead, the focus stayed on capability and speed, while the risk conversation came later, after exposure had already occurred. AI implementation is failing because it is being treated like a feature rather than a highly privileged actor inside the environment. Without defined boundaries, it introduces:
The critical moment comes before deployment, when teams either define the controls needed or skip that step entirely. Once the system is live, everything gets harder to contain, and organizations shift from defining risk to reacting to it. The takeaway isn’t to slow down AI adoption, but to change the order:
2https://www.businessinsider.com/lovable-security-access-vibe-coding-projects-risk-2026-4
The Hidden Cybersecurity Risks of Enterprise AI Implementation
Enterprise AI adoption is accelerating, but security maturity is not keeping pace. In Accenture’s 2025 research of large organizations, 90% were not adequately prepared to secure their AI-driven future, 63% fell into an “Exposed Zone” lacking both strategy and technical capability, and 77% lacked the foundational data and AI security practices needed to protect models, pipelines, and cloud infrastructure.1
That gap matters because AI changes the threat landscape in two directions at once. It gives defenders new tools, but it also gives attackers more speed, scale, and precision. The World Economic Forum reported that 66% of organizations expected AI to have the biggest impact on cybersecurity in 2025, yet only 37% had processes in place to assess the security of AI tools before deployment. In the same research, 72% of respondents said organizational cyber risk had increased, and nearly 47% cited adversarial advances powered by generative AI as a primary concern.2
The most dangerous part is that many of these risks stay hidden until AI is already embedded in workflows. A team adopts a copilot. A department connects an AI assistant to internal knowledge. A vendor quietly adds generative features to an existing platform. On the surface, those are productivity decisions. In practice, they can create new exposure paths for sensitive data, model misuse, compliance failure, and third-party risk. IBM argues that scalable enterprise AI depends on four pillars working together: AI governance, AI security, data governance, and data security. Without all four, trustworthiness and business outcomes are at risk.
1. Shadow AI creates blind spots faster than most leaders realize
One of the biggest risks in enterprise AI is not a malicious actor. It is invisibility.
Employees often start using public or embedded AI tools because they are trying to move faster. They summarize documents, generate drafts, analyze data, or write code. But if those tools are outside approved processes, leadership may have no clear view of what data is being entered, where prompts are stored, what models are being used, or whether outputs are being reused in sensitive workflows. IBM notes that shadow AI significantly complicates the challenge of scaling and securing enterprise AI and cites data showing that organizations with high levels of shadow AI face materially higher breach costs.3
A realistic example looks like a finance analyst pasting contract language into a chatbot to summarize renewal terms; a marketing manager that uses an AI writing assistant with customer segmentation notes; a developer that feeds snippets of proprietary code into a code assistant. None of those actions may feel dramatic in the moment, but together, they can create a quiet pattern of uncontrolled data exposure.
2. Data leakage risk is broader than “someone pasted something sensitive”
When people think about AI risk, they often picture an obvious mistake like an employee entering confidential data into a public model. That risk is real, but it is only part of the story.
The broader issue is that enterprise AI depends on data flows, permissions, retrieval systems, APIs, model connections, logs, and cloud infrastructure. Accenture found that 77% of organizations lacked the essential data and AI security practices needed to protect critical business models, data pipelines, and cloud infrastructure. That means the problem is often structural and not just behavioral.
In other words, even organizations that publish acceptable-use guidance may still be exposed if their underlying environment is not designed for secure AI usage. Weak access controls, poorly governed data sources, insecure integrations, and unclear retention practices can turn a promising AI rollout into a security event waiting to happen. NIST’s AI Risk Management Framework and its Generative AI Profile were created to help organizations identify and manage exactly these kinds of cross-cutting risks in a structured way.
3. Third-party AI risk is now part of normal vendor risk
Many enterprises are not building every AI capability from scratch. They are consuming AI through SaaS platforms, copilots, cloud providers, security tools, and line-of-business applications.
That means AI risk is increasingly arriving through vendors. The challenge is that many vendor review processes were built for traditional software, not for tools that generate content, access internal knowledge, retain prompts, or rely on opaque external models. The World Economic Forum found that only 37% of organizations had processes to assess the security of AI tools before deployment, even as AI adoption accelerated.
This creates a familiar but more complex version of third-party risk. Security teams now need to ask not only where data is hosted, but also how models are trained, whether prompts are retained, how outputs are monitored, what guardrails exist, and whether one vendor’s feature depends on another upstream provider. If those questions are skipped, organizations can inherit risk they never explicitly approved.
4. AI makes social engineering more scalable and convincing
Another hidden risk is that enterprise AI implementation is happening at the same time adversaries are upgrading their own capabilities.
The World Economic Forum reported that generative AI is augmenting cybercriminal capabilities and contributing to an uptick in social engineering attacks, with 42% of organizations reporting phishing and social engineering incidents. Nearly half of organizations in its research identified adversarial advances powered by generative AI as a primary concern.
That matters for enterprise AI strategy because the same organization adopting AI internally may also be facing more convincing phishing emails, better impersonation, faster content generation, and more scalable attack campaigns externally. AI implementation is not happening in a vacuum. It is happening while the offensive environment is getting more efficient too.
A practical scenario is when a help desk receives a flawless reset request written in the tone of an executive, referencing real internal project language scraped from prior leaks or public sources. The email looks ordinary. The speed and quality behind it are not.
5. Security is still being invited in too late
In many organizations, the business starts with the use case and asks security to review it later. By then, the AI tool may already be integrated into workflows, connected to internal systems, or used by multiple teams.
Accenture found that only 28% of organizations embed security into transformation initiatives from the outset, and fewer than half strike a balance between AI development and security investment. That reactive model forces teams to retrofit controls later, usually under time pressure.
This is where enterprise AI projects often become expensive to fix. Security is asked to solve for logging, permissions, data boundaries, human review, vendor questions, and policy enforcement after business teams have already committed to speed and scale. What looked like an implementation project turns into a governance and architecture cleanup exercise.
6. Fragmented ownership turns risk into an operating problem
The hidden cybersecurity risks of AI are harder to manage when governance and security are siloed. IBM warns that fragmented approaches lead to inconsistent risk assessments, conflicting priorities, weak visibility into AI usage, and exposure to bias, drift, shadow AI, data misuse, noncompliance, and hacking.
That point is easy to underestimate. Many organizations do have smart people thinking about AI risk. Legal is reviewing policy. Security is reviewing access. Data teams are reviewing quality. Procurement is reviewing vendors. But if those functions are not coordinated, risk does not disappear. It gets distributed, which is exactly what makes AI exposure harder to see until something breaks.
What leaders should do now
The answer is not to slow AI to a crawl, rather to make AI implementation harder to do unsafely.
A practical response usually starts with five moves:
Final thought
The hidden cybersecurity risks of enterprise AI are not hidden because they are rare. They are hidden because they often look like ordinary business adoption right up until they create an incident.
That is why AI security has to be treated as an implementation requirement rather than a cleanup task. The organizations that benefit most from AI will not be the ones that move fastest without controls. They will be the ones that scale with visibility, governance, and security built in from the start.
1https://newsroom.accenture.com/news/2025/only-one-in-10-organizations-globally-are-ready-to-protect-against-ai-augmented-cyber-threats
2https://www.weforum.org/stories/2025/01/the-3-steps-to-accurate-and-trustworthy-enterprise-ai/
3https://www.ibm.com/think/insights/cios-ai-risk-governance-gap
Artificial intelligence is reshaping cybersecurity faster than most organizations can adapt. In 2026 already, multiple reports from Google, IBM, Deloitte, and independent security researchers confirmed what many security leaders already suspected: AI is no longer just a defensive tool. It is now embedded across the entire attack lifecycle.
At the same time, AI is becoming essential to detection, triage, and response. This dual reality presents a challenge that is not purely technological, but also operational and human.
AI Is Accelerating Adversary Capabilities
Recent research shows that threat actors are already operationalizing generative AI.
Google reported that nation-state–backed hackers are actively using its Gemini models to accelerate reconnaissance, develop phishing content, and research vulnerabilities faster than traditional methods allowed. While AI did not replace malware development outright, it significantly reduced the time and effort required to move from idea to execution.1
This aligns with broader industry observations that AI lowers the barrier to entry for sophisticated attacks. Phishing campaigns are becoming harder to detect, social engineering is more targeted, and attackers can iterate rapidly without the need for deep technical expertise.
AI Is Also Becoming Critical to Defense
On the defensive side, organizations are increasingly relying on AI to manage scale.
Google’s Cloud CISO Perspectives report highlights how AI is now embedded in security operations to help teams analyze massive volumes of telemetry, identify anomalies, and reduce alert fatigue. AI enables faster prioritization and response, particularly in environments where manual analysis is no longer feasible.2
IBM’s cybersecurity predictions for 2026 reinforce this trend, noting that AI-driven automation is becoming essential as security teams face growing attack surfaces and persistent staffing shortages. AI can augment analysts, but it cannot operate effectively without experienced humans guiding and validating its output.3
The AI Skills Gap Is Now a Security Risk
While AI tools are proliferating, the expertise required to deploy and secure them safely is not.
Deloitte’s analysis of AI in cybersecurity describes a growing dilemma: organizations want the efficiency gains AI promises, but they lack the internal expertise to govern models, secure AI pipelines, and prevent misuse. Poorly implemented AI can introduce new vulnerabilities, data leakage risks, and compliance challenges.4
Adding to this concern, Financial Management (FM) Magazine reports that AI-related vulnerabilities are now among the fastest-growing cyber risks identified by executives. These include model manipulation, prompt injection, data poisoning, and abuse of AI-enabled workflows.5
In short, AI expands both capability and complexity. Organizations must now defend traditional infrastructure, cloud environments, and a new layer of AI systems, often without having dedicated AI-security specialists on staff.
Why People Still Matter in an AI-Driven Security Program
Despite the power of AI, these reports consistently point to one conclusion: human expertise remains critical.
AI can prioritize alerts, but humans decide risk tolerance. AI can flag anomalies, but humans interpret business impact. AI can automate response, but humans design the controls that prevent automation from causing harm.
This is where many organizations encounter friction. Hiring permanent, specialized AI security talent is difficult, time-consuming, and expensive. Yet delaying expertise while threats evolve is not a viable option.
Staff Augmentation as a Practical Response
As AI reshapes cybersecurity, staff augmentation has emerged as a pragmatic way for organizations to adapt.
Rather than overextending existing teams or waiting months to hire niche talent, organizations can bring in experienced security professionals who already understand AI-driven threats and defenses. These specialists can help with:
This model allows organizations to move forward with AI adoption while managing risk responsibly.
Looking Ahead
AI is not a future concern. It is a present reality shaping how cyberattacks are launched and how defenses are built. The organizations that succeed will be those that combine advanced technology with experienced human judgment.
As the cybersecurity landscape evolves, flexibility in how teams are built and supported will be just as important as the tools they deploy.
1https://thehackernews.com/2026/02/google-reports-state-backed-hackers.html
3https://www.ibm.com/think/news/cybersecurity-trends-predictions-2026
5https://www.fm-magazine.com/news/2026/jan/ai-vulnerabilities-emerge-as-fastest-growing-cyber-risk/
Cybersecurity teams across every industry are facing the same reality: demand is rising, threats are accelerating, and qualified talent remains difficult to hire and retain. Despite increased awareness and investment, the cybersecurity workforce shortage continues to constrain organizations’ ability to manage risk effectively.
Recent U.S.-focused industry research confirms that this challenge is not temporary. It is structural.
The Cybersecurity Talent Gap Is Still Widening
According to the ISC2 2025 Cybersecurity Workforce Study, organizations continue to report significant skills gaps, particularly in hands-on technical roles, cloud security, and incident response. Budget limitations and slow hiring cycles further compound the problem, leaving teams understaffed even as responsibilities expand.1
Similarly, ISACA’s 2025 State of Cybersecurity report highlights that adaptability and practical experience are among the most in-demand skills, yet many organizations struggle to develop or hire for them quickly enough. As a result, existing staff are often asked to stretch beyond their capacity, increasing burnout and operational risk.2
These challenges are not limited to the private sector. A recent U.S. report notes that the Department of Defense alone continues to face tens of thousands of unfilled cybersecurity positions, underscoring how difficult it is to recruit and retain cyber talent at scale.3
Why Traditional Hiring Models Are Falling Short
Conventional hiring approaches are often too slow for modern cybersecurity needs. Recruiting cycles can take months, and even successful hires require onboarding and ramp-up time before they can contribute meaningfully. During that gap, security programs do not pause. Vulnerability backlogs grow, compliance deadlines approach, and incident response workloads intensify.
In many cases, organizations do not need permanent headcount for every security function. Instead, they need timely access to specific expertise, whether that is penetration testing, risk assessments, compliance support, or temporary leadership coverage during periods of transition.
Where Staff Augmentation Fits In
Staff augmentation offers a flexible, practical way to strengthen cybersecurity teams without waiting for long hiring cycles to conclude. By supplementing internal teams with experienced professionals, organizations can:
This model allows organizations to adapt their security capacity to real-world needs rather than fixed staffing assumptions.
Making Staff Augmentation Effective
To be successful, staff augmentation must be implemented thoughtfully. Clear role definitions, integration with existing workflows, and defined objectives are essential. Augmented professionals should complement internal teams, not operate in isolation. Organizations that treat staff augmentation as part of a broader security strategy tend to see better outcomes than those that use it only as a short-term fix.
Industry research consistently shows that blended teams, combining internal knowledge with external expertise, are better positioned to respond to evolving threats while maintaining long-term resilience.
Looking Ahead
The cybersecurity workforce shortage is unlikely to resolve quickly. As threats continue to grow in complexity and volume, organizations need staffing models that provide both agility and expertise. Staff augmentation has become a key component of that strategy, helping teams stay effective even when traditional hiring cannot keep pace.
For cybersecurity leaders, the question is no longer whether staffing challenges exist, but how to design programs that remain resilient despite them.
1https://www.isc2.org/Insights/2025/12/2025-ISC2-Cybersecurity-Workforce-Study
2025 was a defining year for cybersecurity in the United States. Major breaches, ransomware attacks, and nation-state activity dominated headlines. These incidents stood out not for their originality, but for how consistently they revealed the same underlying flaws. From healthcare and insurance to government and global enterprises, the message was clear that cyber risk is no longer just an IT issue but an operational, financial, and reputational one.
Below, we break down some of the most widely covered U.S. cybersecurity news stories of 2025, the key lesson from each, and what organizations should be doing differently heading into 2026.
1. Change Healthcare / UnitedHealth Breach
The U.S. Health Department revealed that the 2024 ransomware attack on Change Healthcare, a technology subsidiary of UnitedHealth Group, exposed data for roughly 190 million Americans, making it the largest healthcare breach in U.S. history. Because the platform sat at the center of healthcare operations, the breach cascaded across insurers, hospitals, and pharmacies, exposing data at unprecedented scale.1
Lesson learned:
Third-party technology is now core infrastructure. When vendors sit deep inside healthcare workflows, a single compromise can ripple across the entire ecosystem.
What to do:
Organizations must treat vendor access like internal access, requiring segmentation, continuous monitoring, and regular risk reassessments.
2. Aflac Data Breach
Insurance giant Aflac disclosed that 22.6 million records containing social security and health information were exposed in a cyberattack. As investigators worked to determine the scope, the delay between intrusion and public disclosure increased the risk of identity theft and fraud for impacted individuals and intensified regulatory and legal scrutiny. It took six months for Aflac to identify all records and to report the extent of the damage.2
Lesson learned:
Delayed detection and disclosure amplify damage. The longer attackers remain undetected, the greater the financial, legal, and trust fallout.
What to do:
Improve detection speed, tighten identity controls, and ensure incident response teams can act decisively under pressure.
3. U.S. Federal Court Systems Targeted
U.S. federal courts reported attempted intrusions aimed at disrupting or accessing judicial systems. While no catastrophic outage was confirmed, the incidents highlighted how even partially successful attacks against public institutions can threaten trust, continuity of government operations, and sensitive legal data.3
Lesson learned:
Critical infrastructure remains a prime target. Government systems face persistent threats from both criminal and nation-state actors.
What to do:
Defense-in-depth, modernized monitoring, and skilled security operations staff need to be prioritized. They are no longer optional. They’re essential.
4. Microsoft Report on AI-Driven Cyber Threats
Microsoft has observed nation-state actors using AI to generate more convincing phishing campaigns, automate reconnaissance, and rapidly adapt attack techniques. These tools enabled adversaries to scale operations faster than traditional security teams could manually respond, increasing both the volume and precision of the attacks.4
Lesson learned:
AI has lowered the barrier to sophisticated attacks. Threat actors can now scale personalization and speed at unprecedented levels.
What to do:
Security teams must match this pace, leveraging automation, behavioral analytics, and threat intelligence to keep up.
5. The U.S. Department of Justice Charges in China-Linked Cyber Espionage
The U.S. Department of Justice charged individuals linked to a Chinese state-sponsored cyber-espionage campaign that targeted U.S. government agencies and private companies over an extended period. The attackers relied on stealthy techniques and long dwell times, often remaining undetected while quietly exfiltrating sensitive information.5
Lesson learned:
Attribution doesn’t stop attacks. Legal action raises awareness, but organizations still need to defend against well-resourced, patient adversaries.
What to do:
Prepare for long dwell times, stealthy lateral movement, and data-exfiltration scenarios. Ransomware is not the only culprit.
6. Major Third-Party Analytics Breach (ShinyHunters-linked)
In a major third-party analytics breach tied to the ShinyHunters group, attackers exploited access to a shared SaaS platform to extract massive volumes of user data. Organizations affected had not been directly compromised themselves, but inherited risk through trusted external services.
Lesson learned:
Your security posture is only as strong as your weakest vendor.
What to do:
Continuously assess third-party risk, not just during onboarding, but throughout the vendor lifecycle.
A Common Thread: The Cyber Talent Gap
Across all the cited news stories, one theme stands out. Organizations did not fail because they didn’t care about security. They failed because they did not have the necessary resources to prevent the attacks.
Many breaches involved:
How Staff Augmentation Helps
Strategic cybersecurity staff augmentation can help organizations:
At Inspire Security Solutions, staff augmentation is not seen as a stopgap, but as a force multiplier that helps organizations keep pace with today’s threat landscape.
Final Takeaway
The cybersecurity stories of 2025 were not isolated incidents. They were warnings.
Organizations that succeed in 2026 and beyond will be those that:
The organizations that emerge the strongest will be those that pair the right technology with the right expertise, building security teams that are as adaptable as the threats they face.
4https://apnews.com/article/ad678e5192dd747834edf4de03ac84ee
As we reflect on 2025, we are reminded just how much we have to be grateful for as a cybersecurity company. The reason isn’t just for growth in our industry, but also because trends emerging in the last three to six months highlight why companies need strong cybersecurity partners now more than ever.
Recent research and news coverage show a clear pattern. Security threats are escalating, cyber talent is harder to hire, and organizations are turning to external experts for reliable, flexible support.
Here are the market realities we are thankful for, and why they ultimately benefit the companies who trust us to strengthen their cybersecurity teams.
1. The Cyber Talent Shortage Is Still Growing, and Companies Need Alternatives
Recent U.S. data continues to paint the same picture. Demand for cybersecurity talent dramatically outpaces supply.
These trends validate the need for flexible cybersecurity partners. Despite a rise in general unemployment in the U.S., the hiring gap for talent in this field is not shrinking anytime soon. Companies need access to vetted, ready-to-deploy cybersecurity professionals without long hiring cycles, high competition, or escalating salary wars.
2. Companies Are Prioritizing Cyber Skills More Than Ever
Businesses are waking up to the reality that cybersecurity is not optional. This shift means organizations are seeking deeper, more specialized expertise.
This shift indicates companies are no longer satisfied with generic IT support. They want specialized cybersecurity skill sets, which is exactly what Inspire can provide. Clients can more quickly and easily access the niche expertise needed to meet modern security challenges without having to build an entire cybersecurity division from scratch.
3. Outsourcing Cybersecurity Talent Is Becoming a Strategic Priority
In the past, outsourcing was viewed as a backup plan, but that’s not the case anymore.
Businesses are recognizing that partnering with a cybersecurity provider is not a cost, rather a force multiplier. Outsourcing empowers organizations to:
It’s a shift that allows them to stay secure and stay focused on what they do best.
4. The Growing Threat Landscape Makes Experienced Partners Essential
Cyberattacks are accelerating at a pace that internal teams often cannot match alone. With identity-driven attacks, supply-chain vulnerabilities, and AI-assisted threats all on the rise, companies need support from experts who track these patterns across multiple environments, not just one. Cybersecurity providers, like Inspire Security Solutions, can deliver context, threat awareness, and rapid expertise that internal-only teams cannot easily maintain.
This benefits clients because they get:
In other words, clients get security that evolves in real time.
In a Challenging Security Climate, There’s Much to Be Thankful For
This year has reminded us that our mission matters, and that the work we do meaningfully protects organizations facing complex threats, limited talent pipelines, and rising pressure to operate securely.
We’re thankful that:
And we’re especially thankful that we get to support organizations when and where they need it most.
In today’s cybersecurity environment, great partners don’t just fill roles. They strengthen resilience.
1https://www.axios.com/2025/07/15/cybersecurity-hiring-fortune-100-expel
3https://cybersn.com/cybersecurity-job-posting-data-report-2025
4https://www.gartner.com/en/newsroom/press-releases/2025-04-22-gartner-survey-finds-85-percent-of-ceos-say-cybersecurity-is-critical-for-business-growth
5https://cyntexa.com/blog/it-staff-augmentation-trends
Hiring cybersecurity talent has become a pressing challenge facing many organizations. The skills gap continues to widen, with reports estimating a global shortage of 4 million cybersecurity professionals.Security leaders are stretched thin, teams are overworked, hiring cycles drag on for months, and budgets are consumed by recruiting fees and employee overhead. 1
That is why Inspire Security Solutions is introducing Inspire Secure: Staff Augmentation, a flexible way to access experienced, U.S.-based security professionals without the delays, costs, or complexity of traditional hiring.
The Three Models of Inspire Secure
Every organization’s needs are different. Inspire Secure offers three levels of service, designed to give you the right balance of control, oversight and partnership.
Inspire Secure: Direct
For organizations that want hands-on control, Inspire Secure: Direct delivers vetted security professionals who work directly under your supervision. You manage their day-to-day work, while Inspire handles candidate sourcing, vetting, onboarding, HR and payroll.
From penetration testers to compliance specialists, Inspire Secure: Direct give you certified talent in weeks, not months. This gives you the flexibility to scale up or down as your needs change.
Inspire Secure: Guided
Inspire Secure: Guided adds Inspire-led oversight to ensure your augmented staff delivers maximum value. You retain strategic control, while Inspire Security Solutions takes on coordination, quality assurance, and performance monitoring.
This model is ideal for organizations struggling with consistency, bottlenecks, or alignment across multiple projects. With a dedicated program manager, standardized workflows, and quarterly performance reviews, Inspire Secure: Guided bridges the gap between staff augmentation and program management.
Inspire Secure: Managed
For organizations that want a turnkey solution, Inspire: Secure provide a fully outsourced security workforce. Inspire Security Solutions takes the responsibility for resource selection, onboarding, management, reporting, and results.
From third-party risk management to compliance monitoring or continuous penetration testing, Inspire Secure: Managed offers predictable performance, outcome-driven delivery and full accountability.
Why Staff Augmentation is More Cost-Effective
Hiring internally comes with hidden costs. Recruiting fees add up quickly, while benefits and overhead can significantly raise the true cost of a new employee. Add a lengthy hiring cycle, and many organizations simply can’t keep up.
By contrast, Inspire Secure provides certified professionals on flexible terms. Whether you need part-time support, project-based help, or full-time resources, Inspire Secure allows you to scale your team quickly, without the long-term commitments or overhead of permanent hires.
Meeting the Challenge Head-on
The cybersecurity threat landscape is evolving rapidly. Organizations cannot afford unfilled positions, overextended teams, or slow onboarding processes. Staff augmentation through Inspire Secure provides the agility to scale, the expertise to deliver, and the cost-efficiency to sustain long-term resilience.
Conclusion
Cybersecurity hiring challenges aren’t going away, but your organization doesn’t have to face them alone. Inspire Secure offers a smarter way to strengthen your defenses with flexible, affordable, and immediate access to the professionals you need.
Whether you choose Direct, Guided, or Managed, Inspire Secure is designed to help you close talent gaps, reduce risk, and keep your business secure.
1 https://www.fortinet.com/corporate/about-us/newsroom/press-releases/2024/fortinet-annual-skills-gap-report-reveals-growing-connection-between-cybersecurity-breaches-and-skills-shortages

